
Chainguard introduced Workspaces, Checks and expanded Libraries protections at Assemble London to secure AI coding agents during execution. Workspaces and Checks are launching in beta, while new Go and. NET Libraries offerings enter Early Access. The move matters because agents can install compromised dependencies or run overprivileged commands while producing useful code.
Isolated execution and verification at Assemble London
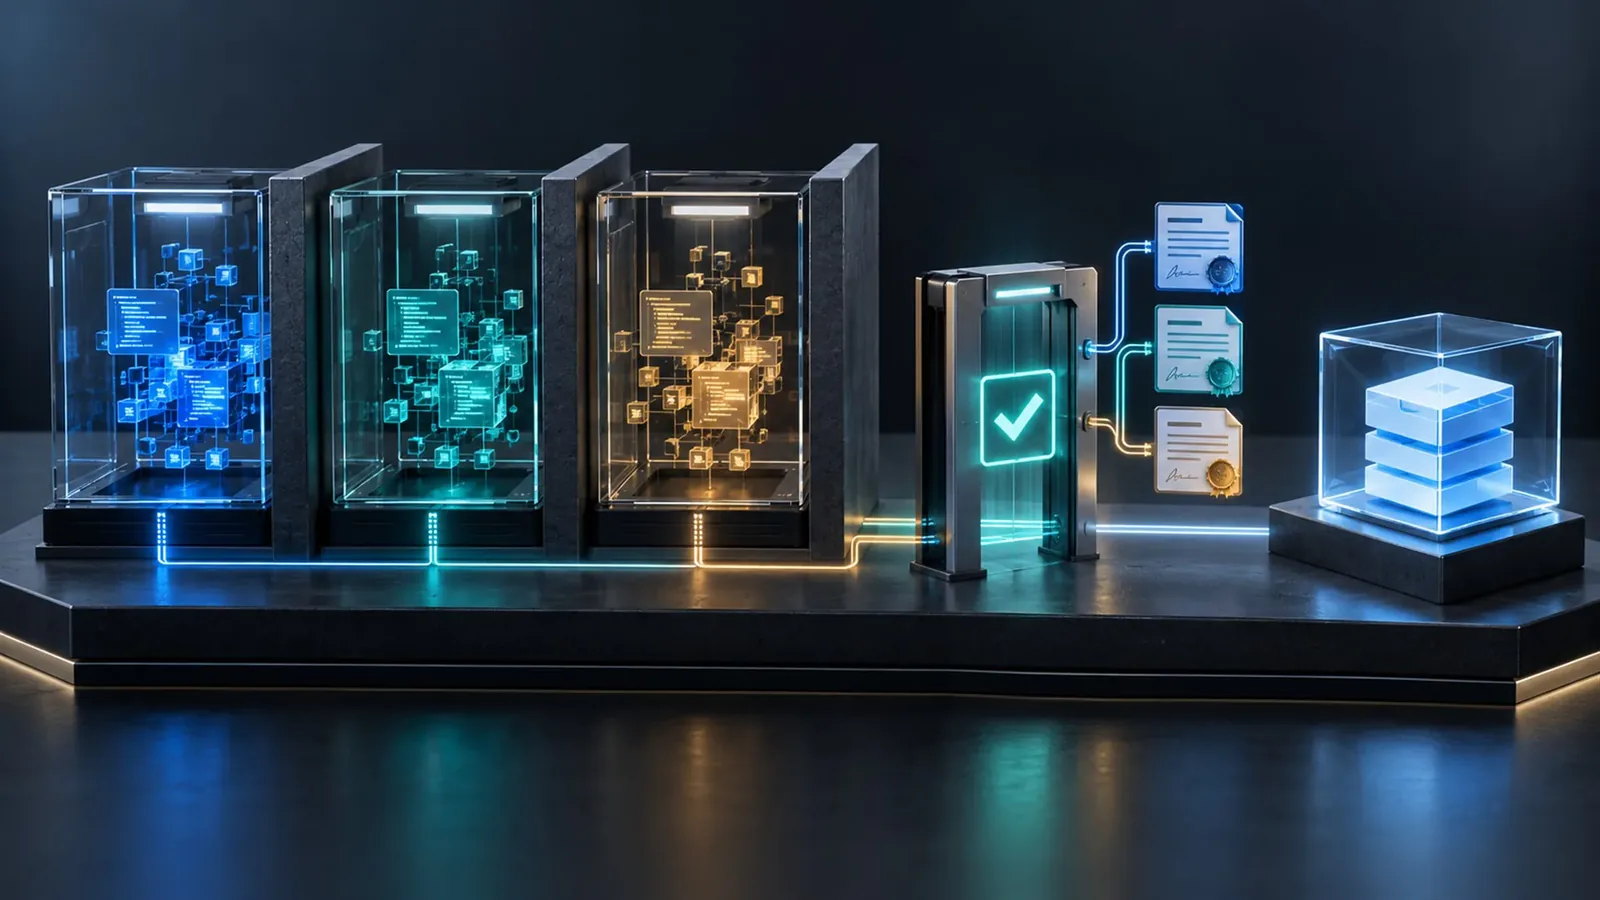
Workspaces gives each developer and agent a separate remote microVM that synchronizes the local working tree, so staff keep their editor and Git workflow while code runs away from the machine. Separate environments allow multiple agents to attempt changes in parallel without sharing one working environment. The release adds credential handling outside the workspace, with encrypted short-lived substitutes for tools that need a credential on disk, plus optional egress policies limiting outbound connections to approved destinations.
Checks is designed as a verification engine inside the agent development loop and works as a tool call paired with Workspaces. The agent session suspends while checks run, then resumes with structured failure logs in its context for another iteration before handoff. Each workflow step runs in its own hardware-isolated microVM, while warm snapshots hold preinstalled dependencies and rebuild when the lockfile changes. A passing run creates a signed attestation linking environment, test result and commit for downstream merge gates.
The launches extend Chainguard OS Packages and Libraries into agent execution. OS Packages are continuously maintained, built from source and supplied with software bills of materials, while environments verify dependencies against the lockfile at runtime. The new Go endpoint adds malware and greyware scanning, configurable package policies and CVE remediation, and the. NET endpoint offers an alternative to direct NuGet consumption. JavaScript and Go gain backported fixes for critical- and high-severity vulnerabilities, and Athena coalition artifacts cover Java and Python flaws found by frontier models on disclosure day.
What this means for companies running coding agents
For teams running parallel agents, hardware isolation plus credential mediation and network policy reduce blast radius when a model follows untrusted content or a dependency turns malicious. Signed records of environment, code changes and check results give security teams an investigable trail instead of an agent summary. Small firms gain a ready-made boundary without building microVM infrastructure, while large firms can standardize approved destinations and credential issuance across many concurrent sessions.
Controls remain only as strong as approved permissions, destinations and tests. Isolation does not make every authorized action harmless, and an attestation proves which checks ran, not that coverage was complete. Chainguard cites results in seconds and lower redundant compute, but launch materials provide no independently validated benchmark across repositories. Buyers should ask which tests are attested, who defines merge-gate policy, and how lockfile verification handles unpinned dependencies.
The marker to watch is beta to production conversion: whether Workspaces and Checks fit real repositories and release policies without adding queues, and whether Early Access Go and. NET endpoints retain policy controls at scale. A separate signal is The AI Exploit Gap survey of 1,300 leaders, where 54% admit leaving high or critical flaws unpatched and 93% fear AI-driven exploit speed. Falling unpatched rates among large firms would show verifiable agent controls easing deployment.
