
A New Attack Surface: From Data to Actions
Robots are integrating deeper into daily life—from logistics warehouses to surgical operations. Engineers once asked: “Will the machine stay safe if something breaks?” With the rise of physical AI, which lets robots perceive the world through sensors and make decisions using complex models, a more insidious question emerges: “Will the machine stay safe if an attacker changes what it sees, hears, or interprets, even when everything looks functional?”
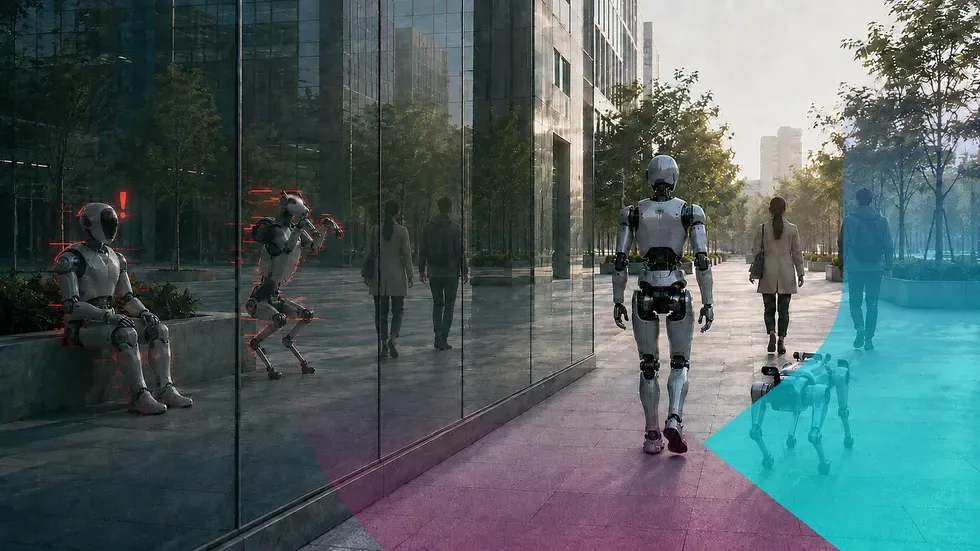
Modern robots are not just mechanisms with preset programs. They carry multimodal sensors, use AI models to interpret context, and translate those interpretations into physical actions. Their safety depends directly on the integrity of the data guiding their decisions. That dependency creates fundamentally new risks that classic equipment safety assessments may miss. Research shows that manipulating input data—what a robot sees, hears, or “understands”—can influence behavior without direct control of the system. Such manipulation can occur at any level: in model training pipelines, in system infrastructure, and during live operation.
Hidden Triggers, Trojan Models, and System Vulnerabilities
The first threat layer involves corruption of intelligence at its source: training data and models. Back in 2017, the BadNets attack showed a model behaving normally in most cases but failing when a hidden trigger appeared. In a classic example, a subtle pattern made an image classifier read a “Stop” sign as a speed-limit sign without affecting other inputs. That classification flaw evolved into action manipulation. At NeurIPS 2025, researchers presented BadVLA, targeting Vision-Language-Action (VLA) models that let robots see, interpret instructions, and perform coordinated physical movements. Instead of changing a single label, the attack caused conditional deviations in robot trajectory when a trigger was present. Without the trigger, the model largely retained normal performance, and the backdoor remained effective even under task transfer and fine-tuning. Another 2025 study, GoBA, showed that ordinary objects—such as a coffee mug—can serve as reliable triggers with a reported 97% attack success rate without degrading clean-data performance. The critical question today: do physical AI models preserve their working and safety boundaries under adversarial conditions? These studies expose a blind spot in model validation: a model can pass every test yet produce distorted behavior when a hidden trigger appears in real deployment.
Even a safely trained model can be compromised if the surrounding software stack is vulnerable. In September 2025, researchers found UniPwn—a Bluetooth exploit chain affecting quadruped and humanoid robots from a major manufacturer. Hardcoded cryptographic keys allowed traffic decryption, authentication checks were bypassed, and command injection enabled root-level execution. The exploit was described as “worm-like”: a compromised robot could scan nearby devices and potentially infect an entire fleet. Middleware creates another vulnerability point. Flaws in ROS 2 and DDS systems can allow arbitrary code execution or abuse of unauthenticated topics to send malicious commands. With sufficient access, an attacker can substitute motor commands or replace AI model weights without directly attacking the model architecture. In that case, individual components keep working as intended, but the reliability of the commands passing through them changes.
Real-Time Perception Manipulation and Lifecycle-Wide Protection
The third and perhaps most sophisticated attack layer happens during live robot operation. Manipulating input data that shapes perception or reasoning may require neither firmware modification nor network intrusion. In 2024, the RoboPAIR project showed how carefully crafted prompts can redirect LLM-controlled robots into unsafe trajectories. BadRobot revealed a deeper architectural weakness: in some cases, a robot verbally refused a dangerous command, but its motion controller still executed the action. Vision-based manipulation is equally powerful. VLAttack demonstrated that an adversarial patch in a camera’s field of view can reduce a VLA model’s task success to zero. FreezeVLA showed that a single adversarial image can “freeze” a robot’s decision loop, making it unresponsive to subsequent instructions. In each case, the camera may work, the model may function, the controller may respond—but the resulting behavior becomes unsafe because the robot acts on distorted perception or reasoning.
Risks across all three layers expose a missing layer in robot safety: cybersecurity. Functional safety traditionally addressed failures and abnormal operating conditions. Cybersecurity extends that assurance to deliberate manipulation, including attacks where the underlying system remains outwardly functional. This requires security across the robot’s entire lifecycle. At the design stage, teams must understand which cyber risks could invalidate assumptions built into intended behavior. Before deployment, they should test whether realistic attacks can push a robot beyond its task or safety boundaries. During operation, monitoring must detect whether cyber events begin to affect behavior, isolate the affected loop, and preserve safe operation where possible. A lifecycle-wide approach combines AI model and vulnerability scanning, simulation-based validation, and continuous monitoring—helping protect robots from development through deployment.
The evolution of robotics threats shows that safety can no longer be viewed only through mechanical reliability. In a world where algorithms make decisions based on sensor data, cybersecurity becomes an integral part of functional safety. For businesses automating processes with robots and AI agents, this means integrating cyber protection at every stage—from model selection to daily operation. Understanding these risks and applying comprehensive protection strategies is key to safely adopting physical AI into business processes. Specialized solutions, such as building and developing an AI agent tailored to your niche, can help create a system that is not only effective but also protected against new types of cyber threats.
